
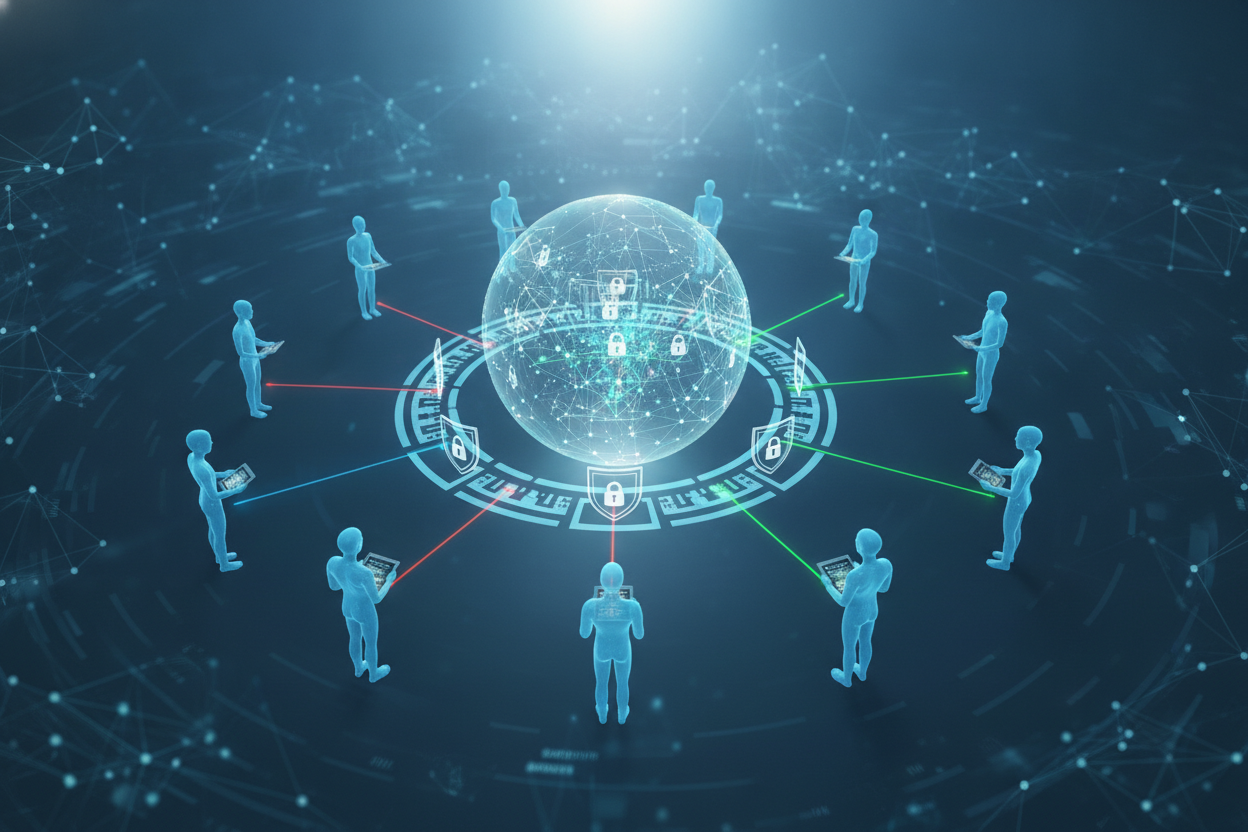
Zero trust has become one of the most important ideas in modern cybersecurity, but it is often misunderstood. At its core, zero trust means never assuming access is safe simply because it comes from inside the network. Every request should be verified, and permissions should be limited to what is needed for the task at hand.
This approach matters because traditional network boundaries are no longer enough. Employees work from different locations, apps live across multiple cloud platforms, and sensitive data moves through countless devices and services. When access controls rely on outdated assumptions, attackers can exploit that trust. Zero trust reduces the blast radius by treating each connection as a potential risk until proven otherwise.
Implementation usually starts with identity, device posture, and least-privilege access. Organizations may add multi-factor authentication, conditional access, and continuous monitoring to strengthen their defenses. These changes do not need to happen all at once. In many cases, a phased rollout is more realistic and easier for users to adopt.
For business leaders, zero trust is not just a security framework; it is a mindset shift. It encourages better visibility, stronger controls, and more resilient operations. MemoisElle’s audience will appreciate that it aligns security with the way modern work actually functions, where data and users are rarely confined to one place.
Leave a Reply