
Cookie Notice Plugin in 2026: 7 Live Checks Before You Trust One
A useful guide to cookie notice plugin should help readers understand both the rule and the behavior behind the rule. That is where consent topics become genuinely practical instead of sounding like recycled compliance copy.
The practical review for cookie notice plugin starts when you look past the banner copy and test the live behavior. That is usually where teams find the real gaps: tags firing too early, weak refusal flows, and settings that drift after routine site changes.
A cookie notice plugin sits between your live site and the technologies that store or access information on a device. The plugin may control a banner, a preference center, script timing, revisit links, category labels, consent records, or links into the privacy policy.
This is why the official guidance still matters more than the vendor demo. The ICO says you “cannot set non-essential cookies” before consent and that users should have the “means to enable or disable non-essential cookies” easily. CNIL says “rejecting cookies should be just as easy as accepting them.” WordPress says site administrators must keep privacy information “current and accurate,” and the Plugin Handbook says a plugin handling personal data “should add a section of suggested text” to the privacy policy helper. In California, the CPPA says a person may opt out of sale or sharing through a “user-enabled opt-out preference signal.”
If you want the closest companion reads first, start with these guides to WordPress cookie notice, cookie consent plugin, and website privacy checker. This page stays narrower. It is the cookie notice plugin review I would use this week before trusting one on a live site.
If your team is trying to get cookie notice plugin under control without adding a heavyweight privacy stack, DataShyre can help. DataShyre focuses on consent and preference management that are easier to implement, easier to operate, and easier to trust on a live site. Start with DataShyre’s consent and preference management or book a demo.
If your team needs help testing the runtime behind the banner, DataShyre can help with consent implementation review, policy alignment, data mapping, and downstream rights workflow cleanup.
1. Define what the cookie notice plugin is actually responsible for
The first cookie notice plugin mistake is acting as if every plugin in the category does the same job.
They do not.
Some mainly provide:
- first-layer banner UI;
- category toggles and preference centers;
- script blocking or deferral;
- region targeting;
- cookie declarations or policy text;
- audit or consent logging;
- integrations with tag managers, analytics, ad tools, or embeds.
Those capabilities are not interchangeable.
A polished banner is not proof that optional tags wait.
A cookie table is not proof that the policy page tells the truth.
A consent log is not proof that rejection is easy.
Before trusting any cookie notice plugin, decide exactly what control surface it owns on your site.
2. Test the first page load before you trust the settings screen
This is still the fastest reality check.
The ICO’s current cookies guidance says you “cannot set non-essential cookies” before consent. So a serious cookie notice plugin review starts with browser behavior on a clean first load:
- open the site in a fresh session;
- do not click the banner yet;
- inspect cookies, storage, requests, and embedded calls;
- see what appears before any positive action;
- repeat on the pages that drive most traffic or conversions.
This matters because optional tracking does not always come from the plugin itself. It can come from theme code, page builders, analytics plugins, marketing scripts, video embeds, map embeds, chat widgets, or a tag manager that loads earlier than expected.
If the cookie notice plugin looks compliant but non-essential technologies still load too early, the implementation is failing at the one moment that matters most.
3. Compare the plugin disclosures against the real stack and policy page
This is where many teams drift into false comfort.
WordPress’s privacy documentation still says administrators must keep the policy “current and accurate.” The Plugin Handbook still says a plugin that collects, uses, stores, or passes user data to a third party “should add a section of suggested text.”
That makes a useful cookie notice plugin question:
does the plugin help your policy page describe the live deployment honestly?
Check whether the plugin and policy together explain:
- what categories are actually active;
- which third parties or services receive data;
- what happens before consent, after consent, and after refusal;
- how people revisit or withdraw a choice later;
- whether region-specific behavior changes anything material.
If the banner is specific but the policy page is stale, generic, or silent about embedded services, the site is still exposed.
4. Make rejection and later withdrawal as obvious as acceptance
This is the design test regulators keep pushing toward operations teams.
CNIL says “rejecting cookies should be just as easy as accepting them.” The ICO also says users should have the means to disable non-essential cookies and that it should be easy to do.
So a real cookie notice plugin review should test:
- reject-all from the first layer when your jurisdictional model requires it;
- category-level preference saves;
- reopening the preference center later;
- withdrawing consent after an earlier accept;
- whether the changed state holds across pages and sessions.
If the cookie notice plugin makes acceptance obvious but pushes refusal into smaller links, extra clicks, or a hidden footer control, the risk is not cosmetic. It is structural.
5. Check the California path too if advertising or sharing is in scope
Not every cookie notice plugin problem is an EU-only problem.
The CPPA’s FAQ says consumers can opt out of sale or sharing, including through a “user-enabled opt-out preference signal.” The California DOJ also says a privacy policy should explain the business’s collection, use, sharing, and sale practices.
So if your site uses ad-tech, retargeting, or any sharing flows, test whether the cookie notice plugin setup also aligns with:
- your privacy policy’s description of sale or sharing;
- the site’s handling of Global Privacy Control or similar signals;
- the actual behavior of downstream tags and vendors after an opt-out;
- the way the site explains privacy choices outside the banner itself.
A cookie notice plugin can help with interface behavior and still leave California-facing opt-out handling unfinished. If your stack is complex, DataShyre can help verify whether the banner, policy, and downstream routing actually match.
6. Test the real pages editors change, not only the homepage demo
Many cookie notice plugin failures happen away from the cleanest template.
They show up on:
- campaign landing pages;
- embedded video or map pages;
- blog posts with third-party widgets;
- popups and lead forms;
- localized or geo-targeted pages;
- checkout or scheduling flows with extra scripts.
That is where the nice plugin demo usually stops helping.
If your site uses WordPress, WordPress itself warns that its privacy helper likely does not include everything collected by third-party services such as analytics, newsletter tools, ad partners, or embedded media. That is a useful reminder even beyond WordPress: a cookie notice plugin should be validated on the pages where marketers and editors actually add things.
7. Treat the cookie notice plugin as a release-controlled system
The long-term cookie notice plugin risk is drift.
The plugin updates. The theme changes. A team adds a new embed. A tag manager publish changes load order. The policy page is edited without checking runtime behavior.
And suddenly the banner promises one thing while the site does another.
This is why a better cookie notice plugin process includes:
- retesting after plugin or theme updates;
- retesting after new tags, embeds, or forms go live;
- checking that linked policy text still matches the real stack;
- verifying reject, revisit, and withdrawal after release changes;
- keeping proof of what the site did in each tested state.
Without that discipline, the cookie notice plugin becomes decoration instead of a control.
A practical cookie notice plugin review for this week
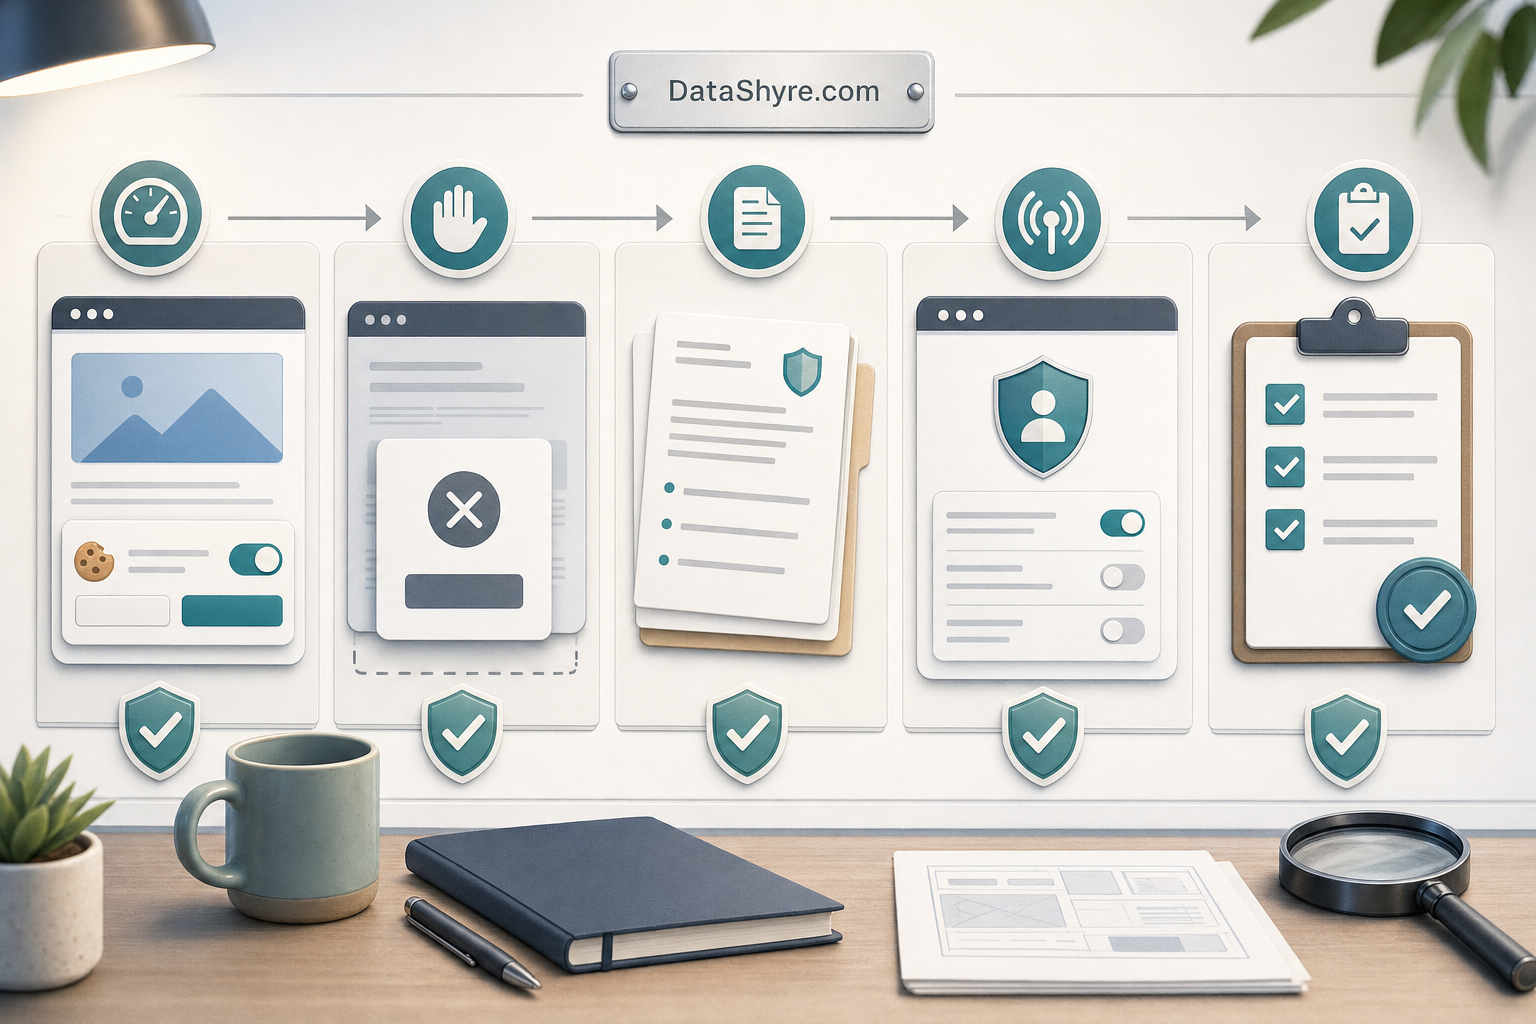
If you were reviewing a cookie notice plugin today, use this order:
- define exactly what the plugin is supposed to control;
- test the first load before any click;
- compare the runtime against the policy page and disclosures;
- test reject, revisit, and withdrawal paths;
- check California opt-out signal handling if ad-tech or sharing is involved;
- retest the pages where editors add embeds, scripts, or forms;
- tie the plugin to release and change-management checks.
That sequence usually tells you more than a feature checklist ever will.
FAQ
Is a cookie notice plugin the same thing as a CMP?
No. A cookie notice plugin may be only one visible layer. A broader consent management platform can also handle cross-site rules, records, mobile flows, downstream preference syncing, and more complex governance.
Can a cookie notice plugin make a site compliant by itself?
Usually not. It can help control banner behavior and some tracking logic, but compliance still depends on accurate disclosures, tested runtime behavior, vendor review, and downstream privacy operations.
If the banner appears before tags load, am I done?
Seen clearly, cookie notice plugin is less about a pop-up and more about whether the site behaves honestly after the visitor makes a choice.
Official sources used
- ICO, Cookies and similar technologies: https://ico.org.uk/for-organisations/direct-marketing-and-privacy-and-electronic-communications/guide-to-pecr/cookies-and-similar-technologies/
- WordPress.org Documentation, WordPress Privacy: https://wordpress.org/documentation/article/wordpress-privacy/
- WordPress.org Documentation, Settings Privacy screen: https://wordpress.org/documentation/article/settings-privacy-screen/
- WordPress Plugin Handbook, Privacy: https://developer.wordpress.org/plugins/privacy/
- WordPress Plugin Handbook, Suggesting text for the site privacy policy: https://developer.wordpress.org/plugins/privacy/suggesting-text-for-the-site-privacy-policy/
- CNIL, Dark Patterns in Cookie Banners: https://www.cnil.fr/en/dark-patterns-cookie-banners-cnil-issues-formal-notice-website-publishers
- California Privacy Protection Agency, FAQs: https://www.cppa.ca.gov/faq.html
- California Department of Justice, California Consumer Privacy Act (CCPA): https://oag.ca.gov/privacy/ccpa